From Anita’s desk
Anita Patel
Minerva Tec Group
Summer is when businesses slow down, but attackers don't take the season off. In this June 2026 issue, I'm asking the question that keeps coming up in my conversations with leaders: who is watching your business while you're away?
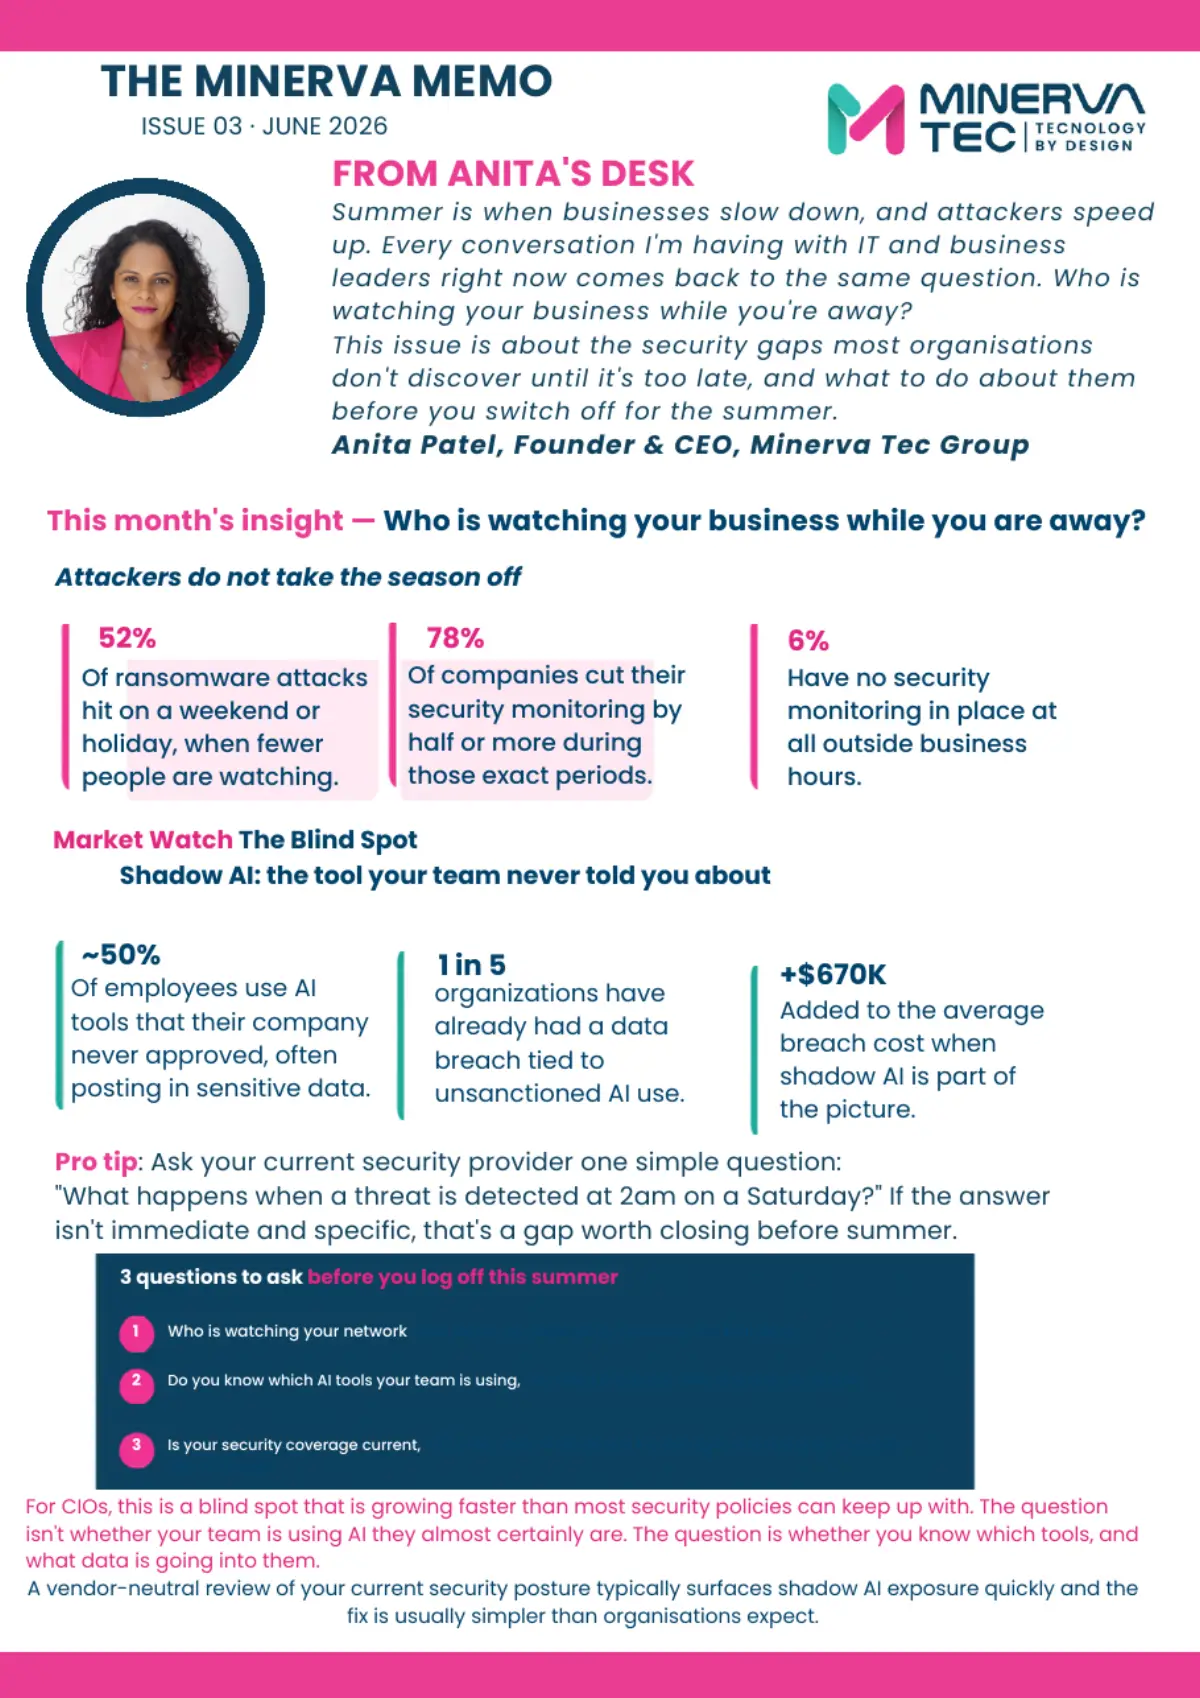
52%
Ransomware attacks on weekends or holidays
78%
Companies halving monitoring during those periods
6%
No security monitoring outside business hours
Who is watching after hours?
This issue reports that 52% of ransomware attacks hit on weekends or holidays, while 78% of companies cut security monitoring by half or more during those periods. Another 6% have no monitoring outside business hours.
Ask your provider: ‘What happens when a threat is detected at 2am on a Saturday?’ If the answer isn't immediate and specific, that's a gap worth closing before summer.
Market watch: the shadow AI blind spot
The figures in this issue indicate that around 50% of employees use unapproved AI tools, often entering sensitive data. One in five organisations has already had a breach tied to unsanctioned AI use, with shadow AI adding $670K to the average breach cost.
The question isn't simply whether your team uses AI, but which tools they use and what data goes into them. A vendor-neutral security review can help expose this risk.
- Who watches your network after hours, on weekends, and over holidays?
- Which AI tools does your team use, and what company data goes into them?
- Is your security coverage current, or auto-renewing with unreviewed gaps?
Partner spotlight: who's in our corner
AgileBlue combines AI-driven detection, investigation, and response with a 24/7 US-based security operations centre. It covers endpoints, Microsoft 365, cloud, email, and networks; most organisations are onboarded in under two weeks. This issue offers the first three organisations to schedule a discovery call a complimentary Threat Exposure Snapshot covering leaked credentials, exposed assets, and external risks.
Cyber Defense Group (CDG) provides cybersecurity consulting and virtual CISO services for mid-size businesses, with clear deliverables and predictable pricing. Its work includes risk assessments, compliance readiness, AI governance, and incident response.
eSentire provides managed detection and response to over 2,000 organisations across 80 countries, combining 24/7 threat hunting, AI-driven detection, and hands-on response. Its services support mid-size organisations addressing cyber insurance requirements and board-level security expectations.
Ask Anita: where do we start with an insurance-flagged gap?
Start with visibility. Understand what is monitored, what isn't, and where your biggest exposures are. A vendor-neutral review provides a prioritised starting point. You don't need to fix everything at once, but you do need to know what to fix first.
Have a question? Get in touch. I read every one.
Key takeaways
- Confirm who detects and responds to threats outside business hours.
- Identify unapproved AI tools and the data being shared.
- Review coverage rather than letting security contracts renew unchecked.
- Prioritise security fixes based on visibility into your exposures.
View the original document (2 pages)